Why Southeast Asia’s Crypto Patchwork is a Double-Edged Sword

Why Southeast Asia’s Crypto Patchwork is a Double-Edged Sword

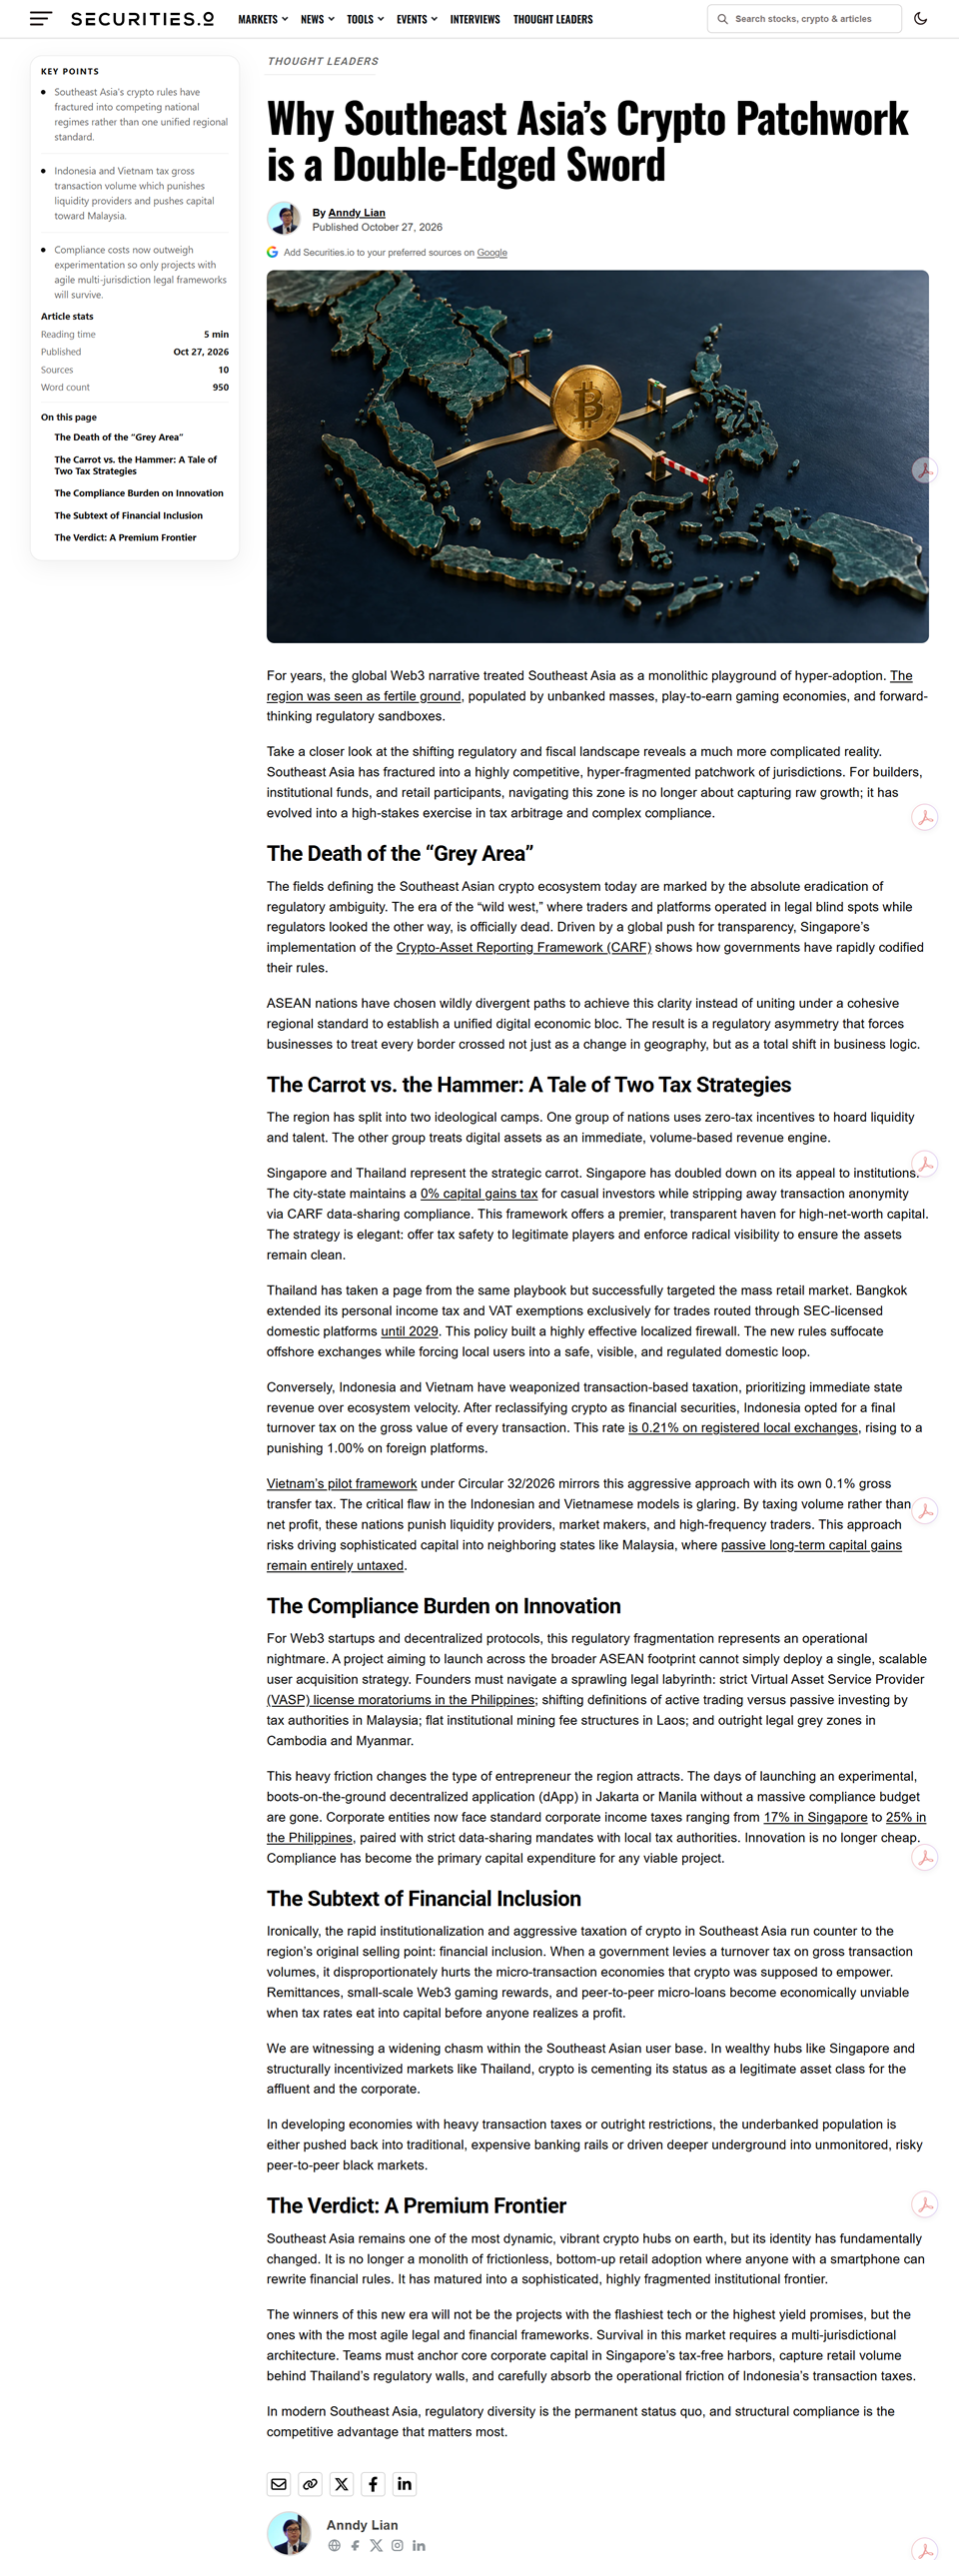
For years, the global Web3 narrative treated Southeast Asia as a monolithic playground of hyper-adoption. The region was seen as fertile ground, populated by unbanked masses, play-to-earn gaming economies, and forward-thinking regulatory sandboxes.

Take a closer look at the shifting regulatory and fiscal landscape reveals a much more complicated reality. Southeast Asia has fractured into a highly competitive, hyper-fragmented patchwork of jurisdictions. For builders, institutional funds, and retail participants, navigating this zone is no longer about capturing raw growth; it has evolved into a high-stakes exercise in tax arbitrage and complex compliance.

The Death of the “Grey Area”

The fields defining the Southeast Asian crypto ecosystem today are marked by the absolute eradication of regulatory ambiguity. The era of the “wild west,” where traders and platforms operated in legal blind spots while regulators looked the other way, is officially dead. Driven by a global push for transparency, Singapore’s implementation of the Crypto-Asset Reporting Framework (CARF) shows how governments have rapidly codified their rules.

ASEAN nations have chosen wildly divergent paths to achieve this clarity instead of uniting under a cohesive regional standard to establish a unified digital economic bloc. The result is a regulatory asymmetry that forces businesses to treat every border crossed not just as a change in geography, but as a total shift in business logic.

The Carrot vs. the Hammer: A Tale of Two Tax Strategies

The region has split into two ideological camps. One group of nations uses zero-tax incentives to hoard liquidity and talent. The other group treats digital assets as an immediate, volume-based revenue engine.

Singapore and Thailand represent the strategic carrot. Singapore has doubled down on its appeal to institutions. The city-state maintains a 0% capital gains tax for casual investors while stripping away transaction anonymity via CARF data-sharing compliance. This framework offers a premier, transparent haven for high-net-worth capital. The strategy is elegant: offer tax safety to legitimate players and enforce radical visibility to ensure the assets remain clean.

Thailand has taken a page from the same playbook but successfully targeted the mass retail market. Bangkok extended its personal income tax and VAT exemptions exclusively for trades routed through SEC-licensed domestic platforms until 2029. This policy built a highly effective localized firewall. The new rules suffocate offshore exchanges while forcing local users into a safe, visible, and regulated domestic loop.

Conversely, Indonesia and Vietnam have weaponized transaction-based taxation, prioritizing immediate state revenue over ecosystem velocity. After reclassifying crypto as financial securities, Indonesia opted for a final turnover tax on the gross value of every transaction. This rate is 0.21% on registered local exchanges, rising to a punishing 1.00% on foreign platforms.

Vietnam’s pilot framework under Circular 32/2026 mirrors this aggressive approach with its own 0.1% gross transfer tax. The critical flaw in the Indonesian and Vietnamese models is glaring. By taxing volume rather than net profit, these nations punish liquidity providers, market makers, and high-frequency traders. This approach risks driving sophisticated capital into neighboring states like Malaysia, where passive long-term capital gains remain entirely untaxed.

The Compliance Burden on Innovation

For Web3 startups and decentralized protocols, this regulatory fragmentation represents an operational nightmare. A project aiming to launch across the broader ASEAN footprint cannot simply deploy a single, scalable user acquisition strategy. Founders must navigate a sprawling legal labyrinth: strict Virtual Asset Service Provider (VASP) license moratoriums in the Philippines; shifting definitions of active trading versus passive investing by tax authorities in Malaysia; flat institutional mining fee structures in Laos; and outright legal grey zones in Cambodia and Myanmar.

This heavy friction changes the type of entrepreneur the region attracts. The days of launching an experimental, boots-on-the-ground decentralized application (dApp) in Jakarta or Manila without a massive compliance budget are gone. Corporate entities now face standard corporate income taxes ranging from 17% in Singapore to 25% in the Philippines, paired with strict data-sharing mandates with local tax authorities. Innovation is no longer cheap. Compliance has become the primary capital expenditure for any viable project.

The Subtext of Financial Inclusion

Ironically, the rapid institutionalization and aggressive taxation of crypto in Southeast Asia run counter to the region’s original selling point: financial inclusion. When a government levies a turnover tax on gross transaction volumes, it disproportionately hurts the micro-transaction economies that crypto was supposed to empower. Remittances, small-scale Web3 gaming rewards, and peer-to-peer micro-loans become economically unviable when tax rates eat into capital before anyone realizes a profit.

We are witnessing a widening chasm within the Southeast Asian user base. In wealthy hubs like Singapore and structurally incentivized markets like Thailand, crypto is cementing its status as a legitimate asset class for the affluent and the corporate.

In developing economies with heavy transaction taxes or outright restrictions, the underbanked population is either pushed back into traditional, expensive banking rails or driven deeper underground into unmonitored, risky peer-to-peer black markets.

The Verdict: A Premium Frontier

Southeast Asia remains one of the most dynamic, vibrant crypto hubs on earth, but its identity has fundamentally changed. It is no longer a monolith of frictionless, bottom-up retail adoption where anyone with a smartphone can rewrite financial rules. It has matured into a sophisticated, highly fragmented institutional frontier.

The winners of this new era will not be the projects with the flashiest tech or the highest yield promises, but the ones with the most agile legal and financial frameworks. Survival in this market requires a multi-jurisdictional architecture. Teams must anchor core corporate capital in Singapore’s tax-free harbors, capture retail volume behind Thailand’s regulatory walls, and carefully absorb the operational friction of Indonesia’s transaction taxes.

In modern Southeast Asia, regulatory diversity is the permanent status quo, and structural compliance is the competitive advantage that matters most.


https://www.securities.io/southeast-asia-crypto-regulation-tax-compliance/
j j j

If Binance says user funds are safe, why did Bitcoin still fall to $77,037.20?

If Binance says user funds are safe, why did Bitcoin still fall to $77,037.20?

Bitcoin fell 4.87% to $77,037.20 in 24 hours and underperformed a broadly weaker crypto sector. A confirmed security incident at Binance on October 29 triggered the drop. That shock arrived against a 65% correlation with the S&P 500. Macro risk aversion had already set a defensive tone. The result was a fear-driven repricing that hit the largest digital asset harder than its peers and exposed how quickly confidence drains when the system’s central counterparty looks vulnerable. 

The breach involved hot wallets. Arkham, Chainalysis, and TRM Labs estimate total outflows ranging from $2B up to $6B. The higher figure would make it the largest cryptocurrency heist in history. Traders sold before the exchange provided full details. That response was rational because the platform anchors a huge share of global crypto liquidity. Changpeng Zhao and co-founder Yi He moved quickly to reassure users. Yi He pledged that the company would cover all hacking losses using its capital margins and its Secure Asset Fund for Users, known as SAFU. Current executives echoed the message that customer funds were safe. Those statements matter. They landed in a market already inclined to distrust reassuring words until on-chain evidence backs them up. Trust in an exchange rests on proof, not press releases, and volatility lives in the gap between the two.

Containment has moved fast. Major crypto entities froze roughly $3B in stolen assets. Tether froze $1.57B. Circle froze more than $800M. Ripple froze $200M. World Liberty Financial contributed additional assets. That coordination is a genuine bright spot and shows the industry’s emergency-response machinery can act when the stakes are high. Binance suspended all deposits and withdrawals while its team conducts security checks. Binance paused trading on the Binance Alpha platform as a precaution. Binance US confirmed it remained entirely unaffected. That detail matters for users in the United States and does little to calm global trading in the immediate term. The exchange said withdrawal access will restore automatically once it fully deploys security patches. Until that happens, uncertainty itself becomes a force that moves prices. Frozen funds reduce the final damage, but they do not restore normal deposit and withdrawal flow.

The secondary driver was mechanical and brutal. The initial slide triggered a cascade of leveraged long liquidations totaling more than $629M in 1 hour. More than 96% of those positions were bullish long bets. That is the signature of an over-leveraged market catching a sudden shock. When long positions close under pressure, selling feeds on itself, pushing prices lower and triggering more liquidations in a feedback loop that has nothing to do with fundamentals and everything to do with positioning. Binance’s native token BNB tumbled more than 7%, underperforming Bitcoin and underscoring how exchange-specific risk radiates outward. The broader crypto sector weakened. Bitcoin’s underperformance relative to that weaker sector points to a specific loss of confidence rather than a uniform risk-off move. The forced selling did not reflect a fresh judgment about long-term value. It reflected a sudden scramble for exits in a crowded trade.

The 65% correlation with the S&P 500 ties this episode to the wider financial system. Crypto does not trade in isolation. A macro-driven selloff in risk assets creates a backdrop where investors already want to reduce exposure, and the Binance shock accelerated that process. When equities weaken and volatility rises, Bitcoin increasingly trades like a high-beta risk asset rather than an uncorrelated hedge. Correlation doesn’t explain the trigger. It explains why the decline gained traction so quickly. A market already leaning defensive needs little push to turn speculation into a rout. The exchange scare supplied the push, and the macro backdrop supplied the slope.

Technically, the picture is stretched but not without structure. Bitcoin’s 14-day relative strength index sits at 24.32, firmly in oversold territory and suggesting immediate selling pressure may be nearing exhaustion. Price is testing a critical support band between $76,264 and $76,476. If that zone holds and Binance provides a verified update that contains the incident, a relief bounce toward the 50-day exponential moving average near $80,789 becomes plausible. The near-term bias remains bearish until price reclaims the $79,282 level, which represents the 50% Fibonacci retracement. A decisive break below $76,264 support would open the path to the next major demand zone near $75,800. That level aligns with the short-term holder cost basis and would likely intensify pain for recent buyers.

My view is that this episode is less about the breach itself and more about the conditions that let 1 security failure trigger a $629M liquidation cascade in 1 hour. The market entered this shock with too much long-side leverage and too little margin for error. That is a structural vulnerability, not an isolated event. The industry’s ability to freeze roughly $3B in stolen assets is impressive and genuinely reduces the final damage. It does not change the fact that hot-wallet concentration remains a systemic risk. Binance’s pledge to cover losses through SAFU and capital margins is the right response. The size of that fund relative to the upper end of the outflow estimates means the public will want more than assurances. It will want a full accounting, independent verification, and a clear timeline for restoring withdrawal access. Until then, every speculative claim will carry outsized weight.

The practical takeaway for anyone watching this situation is to treat speculation and phishing messages as a source of risk rather than a signal. Scams offering refunds or wallet verification are already capitalizing on the chaos. Anyone who acts on those messages risks compounding a trading loss with a personal security breach. The only reliable sources are Binance’s official X account and announcements on its official website. Withdrawal capabilities will return once security patches are fully deployed. That moment will be a more meaningful test of confidence than any intraday bounce. For now, the near-term outlook remains under bearish pressure. The key question is whether Bitcoin can defend the $76,264 to $76,476 support zone following Binance’s official update, or whether a break lower takes price toward $75,800. The answer will depend less on charts and more on whether the exchange can replace fear with verified facts.

https://e27.co/if-binance-says-user-funds-are-safe-why-did-bitcoin-still-fall-to-us77037-20-20261030/

j j j

Stop Chasing Quantum Ghosts. Fix the Lock On Your Front Door First

Stop Chasing Quantum Ghosts. Fix the Lock On Your Front Door First

7 Key Points:

1/ Crypto lost over $2.2 billion (maybe more now) across 288 documented attacks by late September 2026, putting the year on pace to rival the worst on record.

2/ Off-chain attacks accounted for 76 percent of hack losses in the dataset. Private keys and smart contracts were often not the main weak link.

3/ The Trezor impersonation case cost one person $282 million after a fake support contact obtained a seed phrase.

4/ Coldcard lost $112.7 million through a firmware randomness flaw. Investigators said intruders used unrestricted AI models to find and exploit the weakness.

5/ Bitget lost $387.5 million after a third-party zero-day and stolen internal credentials let criminals push fraudulent withdrawals. Kelp DAO lost $292 million from a cross-chain bridge configuration with a single point of failure. Supply chain and configuration risks are central.

6/ AI is already cheap and scalable. CrowdStrike saw an 89 percent surge in AI-enabled threats and 88 percent of vulnerability attacks starting within 48 hours of a public proof of concept. Fortinet recorded a 389 percent rise in ransomware victims.

7/ Quantum planning matters, with experts warning of relevant machines in the 2029 to 2030s range, but it is a multi-year migration problem.


The numbers land on you like a heavy weight. By late September 2026, the crypto industry had already lost more than $2.2 billion across 288 documented attacks. That figure puts this year on pace to rival the worst on record. The headline number tells a misleading story if you stop there. The real story is in the data, and it points to a threat that looks nothing like the one most boardrooms and security teams worry about.

Take a breath and look at the shape of the damage. In January, a single person lost $282 million after an impersonator posing as Trezor support convinced them to hand over a seed phrase. That was not a broken smart contract. That was a human being trusting a voice on the other end of a message. In July, intruders drained $112.7 million from Coldcard hardware wallets by exploiting a firmware flaw that affected how those devices generated randomness. In September, Bitget lost $387.5 million after criminals exploited a zero-day in third-party security products and used stolen internal credentials to push fraudulent withdrawal commands through the exchange’s own systems. In April, Kelp DAO lost $292 million due to a cross-chain bridge configuration that created a single point of failure for bad actors to poison.

Now look at what those incidents have in common. Private keys were not the weak link in most of them. Code was not the only weak link either. The losses moved through trust, through supply chains, and through the tools and people around the code. Off-chain attacks, the kind that compromise credentials, manipulate people, and poison supply chains, accounted for 76 percent of hack losses in the data set behind that $2.2 billion figure. The threat has shifted away from vanilla smart contract exploits and toward the infrastructure and human layers that hold everything together.

That migration matters because it tells us where defense dollars and attention belong right now. It tells us something else, too. The most urgent fight is not the one against a future quantum computer. The most urgent fight is the one against attacks happening today, many of which use artificial intelligence that is already here and already cheap.

The economics explain the shift. A phishing kit costs almost nothing and reaches on thousands of targets in minutes. A compromised vendor account opens a path into every customer the vendor serves. A stolen session token can bypass the password and the second factor in one move. Security teams that still model the adversary as a lone coder hunting for a reentrancy bug are modeling a smaller threat than the one that actually shows up. The intruders who took $2.2 billion this year studied the humans, the vendors, and the tools. They did not wait for a physics breakthrough.

Consider the pace of change. Verizon’s 2026 Data Breach Investigations Report found that 31 percent of confirmed breaches involved exploitation of software vulnerabilities, and that vulnerability exploitation overtook stolen credentials as the primary initial access vector for the first time. CrowdStrike observed an 89 percent surge in AI-enabled cyber threats, with 88 percent of attacks targeting vulnerabilities occurring within 48 hours of a public proof-of-concept release. Fortinet recorded a 389 percent year-over-year increase in ransomware victims as criminals used AI to automate and scale their operations. These are not projections about some distant future. These are measurements of the present.

The Coldcard case shows how directly AI has changed the game. Investigators found that intruders used unrestricted AI models to uncover and exploit a firmware weakness. On the defensive side, Coinkite used frontier AI tools to audit its entire system after the breach and found problems unrelated to the original bug. AI is not waiting for quantum computing to arrive before reshaping the balance between attackers and defenders. It is reshaping that balance right now, and security teams that treat AI as an afterthought are losing ground.

Why does the quantum conversation keep pulling attention away from this? Partly because quantum feels like the ultimate threat, the kind of thing that justifies major strategic planning and long timelines. The Government Accountability Office reports that experts believe a cryptographically relevant quantum computer could arrive as soon as the 2030s. Google warned in March 2026 that one could arrive by 2029. Those warnings deserve attention. Cryptographic migration takes years, and the harvest-now-decrypt-later problem means some data already sits in intruders’ hands. Nobody should dismiss quantum planning as fantasy.

Planning for quantum and defending against today’s attacks are not the same job, and they do not compete for the same urgency. A quantum computer capable of breaking RSA-2048 does not yet exist. An AI-assisted phishing campaign that drains a nine-figure wallet exists today. A supply chain compromise that evades a third-party security product exists today. A social engineering operation that convinces a person to surrender the one secret that protects everything exists today. The losses are not theoretical. They sit on chain, block by block, month after month.

The instinct to talk about quantum first feels prudent, but it gets priorities backward. Quantum is a migration problem with a horizon measured in years. AI-powered attacks on current code and people are an operational problem with a horizon measured in hours. CrowdStrike found that 88 percent of vulnerability attacks began within 48 hours of a public proof of concept. A defender who spends this quarter building a post-quantum roadmap but does not harden the identity layer, audit the supply chain, and train people to recognize impersonation is preparing for the wrong fight at the wrong time.

This is not an argument against quantum readiness. It is an argument about sequence. First, get the current code and the current humans into a defensible position. Treat AI as the primary adversarial capability it already is, not as a curiosity to address after leaders sign off on the quantum migration plan. The 2026 data is screaming a clear message. The billions are not disappearing because someone built a quantum computer. They are disappearing because criminals are using available tools against the weaknesses in the systems and people we rely on right now.


https://www.benzinga.com/opinion/26/10/62597642/stop-chasing-quantum-ghosts-fix-the-lock-on-your-front-door-first

j j j