To truly grasp this evolving timeline, we must examine the mechanics of the current quantum problem. Quantum computing relies heavily on Shor’s algorithm to break elliptic curve cryptography through brute-force computation. Security analysts classify this specific threat horizon as a long-term issue that remains years or decades away. Hardware engineers have demonstrated no physical machine capable of executing this theoretical attack against modern decentralized networks. The quantum narrative requires huge physical breakthroughs that stubbornly refuse to materialize on schedule. Software algorithms require no such hardware leaps to cause severe disruption.
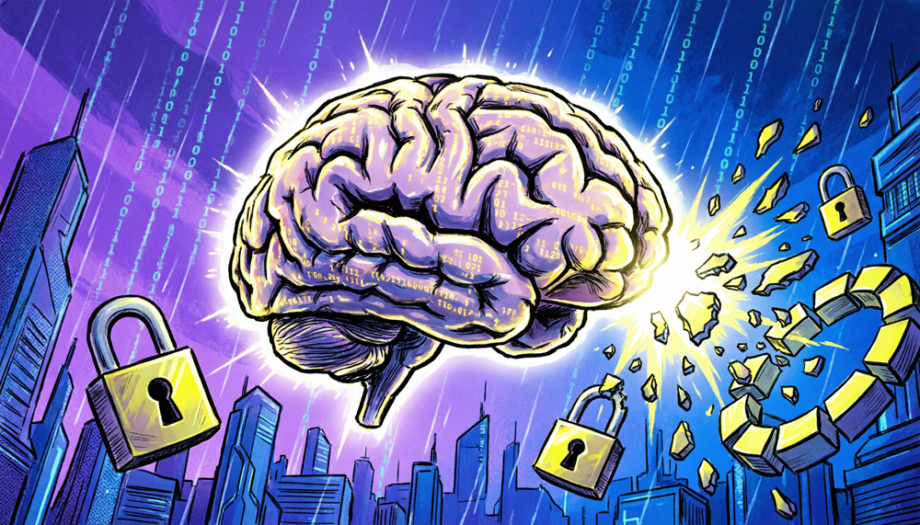
The emerging software threat vector operates fundamentally differently. Machine learning exploits structured mathematical patterns and hidden shortcuts in curves and lattices. Instead of relying on sheer computational brawn, these programs find clever backdoors. The software identifies obscure relationships between numbers that human mathematicians miss completely. During an October 2026 discussion on the platform X, Ethereum researcher Justin Drake warned about this exact scenario. He stated that advanced software could weaken the Elliptic Curve Digital Signature Algorithm within months in a worst-case scenario. Bitcoin and Ethereum both rely heavily on this algorithm to secure user funds.
Ethereum co-founder Vitalik Buterin advanced this discussion further by highlighting a much deeper problem. Developers currently build next-generation defenses using lattice-based cryptography. They designed these frameworks specifically to resist future quantum attacks. Buterin noted that intelligent software could compress 50 years of human mathematical progress into just 2 years. This hyper-accelerated pace of research means algorithms might compromise these supposedly future-proof lattice frameworks before developers finish implementing them. Industry experts confirm this rapidly approaching reality by estimating the theoretical worst-case threat horizon for machine learning math at 2 years.
We must remember why developers chose the Elliptic Curve Digital Signature Algorithm in the first place. Satoshi Nakamoto selected the specific elliptic curve for Bitcoin back in 2009 because it offered strong security with relatively small key sizes. For over 15 years, this mathematical fortress successfully repelled every traditional hacking attempt. Mathematicians trust the discrete logarithm problem operating behind the scenes. They know conventional computers would need millions of years to guess a private key from a corresponding public key. Smart algorithms change this calculus entirely by teaching themselves novel ways to solve the discrete logarithm problem without brute-force guessing.Despite these fascinating theoretical vulnerabilities, digital asset holders have no logical reason to panic today. Theoretical math puzzles differ vastly from practical exploits targeting live decentralized networks. Programmers have engineered no public machine learning attack that successfully cracks a properly generated Bitcoin or Ethereum private key at a practical cost. An artificial neural network identifying a mathematical shortcut in a research paper does not instantly translate into a rogue bot draining billions of $ from active cryptocurrency exchanges. Security researchers monitor these developments closely and continually test the limits of modern software against standard encryption. The defensive walls remain standing. They currently provide 100% protection against all publicly known machine learning attacks.
The most immediate danger to your digital wealth rarely comes from an advanced algorithm. Human error remains the greatest vulnerability in any security system. Reacting impulsively to theoretical software threats often leads to catastrophic financial losses. Vitalik Buterin explicitly advised users against scrambling to move funds immediately. He pointed out that users have historically lost far more money to poorly handled wallet migrations and malicious phishing tools than to actual network hacks. Malicious actors build fake migration tools that promise post-quantum security, only to steal users’ funds the moment a victim connects their wallet.
Instead of executing risky portfolio migrations, asset holders can manage their exposure through simple structural adjustments. The easiest defense is to change how you interact with the underlying blockchain. Cryptocurrency experts highly recommend keeping assets in addresses that have never sent an outbound transaction. When a user creates a new Bitcoin or Ethereum address and only receives funds, the network never exposes the underlying public key on the blockchain. This simple practice adds an incredibly strong layer of structural protection. Even a vastly intelligent learning model cannot attack a public key that remains completely invisible.
Users securing significant wealth should carefully evaluate their multi-signature wallet frameworks. Standard single-signature wallets represent a single point of failure. If an advanced program eventually breaks the underlying cryptography, a standard wallet offers 0 fallback protection. Savvy users opt for off-chain signature collection when designing multi-signature setups. If the primary algorithm fails under extreme computational pressure, a properly designed off-chain signature setup degrades safely to a single signer. This degradation prevents the entire smart contract from opening up to external exploitation. Smart contract architects prioritize this graceful failure mechanism.
The broader decentralized finance industry recognizes these looming challenges and is actively developing countermeasures. Industry roadmaps actively shift toward hash-based alternatives to secure the next generation of financial infrastructure. Developers steer both the Bitcoin and Ethereum networks toward hash-only designs. Technologists look closely at frameworks like SPHINCS and WOTS to provide the next layer of digital security. These hash-based systems lack the structured mathematical patterns that advanced algorithms find so easy to exploit. They offer a fundamentally different approach to protecting sensitive data.
My simple take is this. Understanding the fundamental difference between elliptic curves and hash functions explains why developers place so much faith in the latter. Elliptic curves rely on complex algebraic structures and predictable geometric relationships. A neural network excels at mapping these relationships and discovering hidden geometries. Hash functions operate more like chaotic blenders. You drop data into the hash function, and the underlying algorithm scrambles it into a fixed-length string of characters. No mathematical relationship exists between the input and the final output. Learning models struggle immensely with pure cryptographic chaos because chaos offers absolutely no predictable patterns to analyze. The intersection of digital assets and smart algorithms promises a thrilling narrative over the next 10 years. The cryptocurrency community must remain vigilant as these learning models grow increasingly sophisticated. We must respect the potential for new technologies to rewrite the basic rules of mathematical impossibility. Preparing for these future risks represents an essential evolutionary step for decentralized finance. The developers maintaining Bitcoin and Ethereum possess the talent and the foresight to implement robust defensive upgrades long before theoretical threats become practical exploits. We simply need to exercise patience, practice good operational security, and let the brilliant cryptographers do their crucial work.
Anndy Lian is an early blockchain adopter and experienced serial entrepreneur who is known for his work in the government sector. He is a best selling book author. The latest book is Web4: The Age of Autonomous Intelligence.